All-In-One Security (AIOS) – Security and Firewall Premium Suite
Original price was: $57.00.$11.40Current price is: $11.40.
Every single day, automated bots and malicious scripts crawl the web looking for vulnerable WordPress login pages to exploit. Left unprotected, your website is a constant target for brute-force attacks, comment spam, and content theft. All-In-One Security (AIOS) provides a robust, multi-layered defense system engineered by the team behind UpdraftPlus. Designed for both ease of use and deep technical security, this plugin ensures your digital assets remain safe without bogging down your server’s performance.
With a perfect five-star rating across more than 1 million active installations, AIOS is a widely trusted security option for WordPress. The security engineering team actively tracks emerging vulnerabilities, pushing simultaneous firewall updates to both free and premium users to keep your defenses ahead of modern threats.
Strengthening WordPress Access Control and Login Security
The login page is the primary target for malicious actors. AIOS hardens your WordPress authentication process by replacing default vulnerabilities with strict access protocols:
- Identity Hardening: Detects weak default setups, such as active “admin” usernames or identical login and display names, prompting immediate corrections.
- Login Page Masking: Allows you to configure a custom URL for your WordPress administrative login page, hiding it entirely from automated brute-force bots.
- Database Prefix Modifications: Easily change the default
wp_prefix to disrupt automated SQL injection and targeting scripts. - Smart Login Lockouts: Instantly lock out IP addresses or usernames after a configured number of failed attempts. Admins can view blocked users and restore access with a single click.
- Comprehensive User Auditing: Monitor real-time user activity, tracking active sessions, login/logout timestamps, IP addresses, and failed authentication attempts.
- Forced Session Expirations: Prevent open sessions from remaining active indefinitely by automatically logging out users after a specified period of inactivity.
- Advanced Bot Verification: Integrate Cloudflare Turnstile, Google reCAPTCHA, mathematical CAPTCHA, or hidden honeypot fields on registration and login forms.
- User Enumeration Prevention: Block hackers from scraping author permalinks to harvest registered usernames.
- Multi-Provider Two-Factor Authentication: Out-of-the-box support for Google Authenticator, Microsoft Authenticator, Authy, and other major TFA applications.
- Password Entropy Analysis: Evaluate password strength instantly to determine how long a brute-force attack would take to crack it.
- Emergency Site Lockout: Place your front-end into maintenance mode instantly during core updates or active threat investigations, keeping the back-end accessible to administrators.
- Extended WordPress Salts Security: Inject 64 new randomized characters into your native WordPress Salts and rotate them automatically on a weekly basis to invalidate hijacked cookies.
Advanced Web Application Firewall (WAF) and File Auditing
A Web Application Firewall acts as your site’s perimeter shield, inspecting incoming traffic and dropping malicious requests before they reach your database:
- Progressive Security Levels: Activate firewall rules gradually across basic, intermediate, and advanced tiers to ensure compatibility with your existing plugin stack.
- Real-Time Threat Defenses: Receive automatic firewall updates derived from active exploit tracking managed by the UpdraftPlus security team.
- 6G Blacklist Integration: Built-in 6G Blacklist rules from Perishable Press block bad query strings, malicious request methods, and known bad referrers.
- Fake Googlebot Mitigation: Detect and block malicious scrapers pretending to be official search engine crawlers.
- Granular Blacklisting: Ban specific IP addresses, IP ranges, or user-agent strings from accessing any part of your site.
- XML-RPC Protection: Disable pingback vulnerabilities to prevent your server from being leveraged in distributed denial-of-service (DDoS) attacks.
- Bandwidth Protection: Disable image hotlinking to prevent external domains from stealing your server bandwidth.
- Cross-Site Scripting (XSS) Prevention: Prevent attackers from injecting malicious scripts via malicious cookies.
- File Integrity Monitoring: Automated scanners alert you to any unauthorized file modifications within your core WordPress directory.
- PHP Editor Lockout: Disable the built-in theme and plugin editor in the admin panel to prevent code injection if an administrator account is compromised.
- Directory Permission Audit: Instantly scan for insecure folder permissions and correct them with one-click adjustments.
- Custom Firewall Rules: Advanced developers can inject custom rules directly to restrict access to sensitive server assets.
Content Preservation and Spam Prevention
Protect your hard-earned SEO rankings and user experience by preventing scrapers and spammers from exploiting your pages:
- Anti-Spam Comment Engine: Stop comment spam at the source by blocking submissions originating from external domains. Spammer IPs are permanently banned, and integration with Cloudflare Turnstile or Google reCAPTCHA is available.
- iFrame Protection: Prevent external sites from embedding your content inside frames, protecting your brand from clickjacking attacks.
- Copywriting Protection: Disable right-click, text selection, and copy commands to make manual content theft significantly harder.
- Feed Disabling: Turn off RSS and Atom feeds to prevent automated scraping bots from copying your articles the moment they are published.
- Activity Audit Log: Maintain a clear historical record of site alterations, including theme/plugin installations, updates, activations, and deletions.
Premium Security Upgrades
For high-traffic portals, e-commerce stores, and agency sites, All-In-One Security Premium introduces automated scanning, smart blocking, and priority support.
Deep Malware Scanning and Threat Monitoring
Catching compromises early is vital to maintaining your search engine visibility. If malware is detected, AIOS Premium alerts you immediately:
- Blacklist Monitoring: Daily checks to ensure your domain has not been blacklisted by Google or other major search engines.
- 24-Hour Alerts: Receive detailed email notifications within 24 hours of any malware detection.
- Response Time & Uptime Tracking: Continuous site monitoring checks your server every 5 minutes, notifying you instantly if your site goes offline or suffers latency spikes.
- Flexible Site Management: Easily register, transfer, or remove sites from your scanning dashboard.
Enterprise-Grade Two-Factor Authentication (TFA)
Expand your access control with advanced user management policies:
- Role-Specific TFA: Make TFA mandatory for specific user roles, such as administrators, editors, or shop managers.
- TFA Grace Periods: Require users to set up TFA after their account reaches a specific age (e.g., one week).
- Trusted Device Memory: Allow users to bypass TFA prompts on trusted devices for a set number of days.
- WooCommerce Anti-Bot Protection: Hide sensitive login forms on WooCommerce pages unless active JavaScript is detected on the client browser.
- Customizable Layouts: Style the TFA interface to match your brand’s existing frontend design.
- Emergency Recovery: Generate one-time-use backup codes so users can access their accounts if their primary device is lost.
- Multisite & Third-Party Compatibility: Fully compatible with WordPress Multisite networks. Native integrations work seamlessly with WooCommerce, Affiliates-WP, Elementor Pro, bbPress, and Theme My Login.
Intelligent 404 Mitigation and Geo-Blocking
Block attackers before they find a way in by analyzing their scanning behavior:
- Automated 404 Blocking: Automatically ban the IP addresses of bots scanning your directory structure for non-existent files.
- Country-Level Geoblocking: Restrict traffic based on country of origin using an IP database boasting 99.5% accuracy. Block access to your entire site or specify page-by-page restrictions, while maintaining an IP whitelist for trusted international users.
Premium Support, Translations, and Compliance
- Priority Email Support: Direct access to the technical support desk, with 99% of premium customers receiving a customized response within 24 hours.
- Developer-Friendly Framework: Includes extensive hooks and filters, allowing developers to extend security rules programmatically.
- Local Privacy Compliance: IP addresses collected for brute-force mitigation are stored locally on your own server. No security data is transmitted to third parties or remote server locations.
- Localization Ready: Fully translatable, with official language packs available for English, German, Spanish, French, Hungarian, Italian, Swedish, Russian, Chinese, Portuguese (Brazil), and Persian.
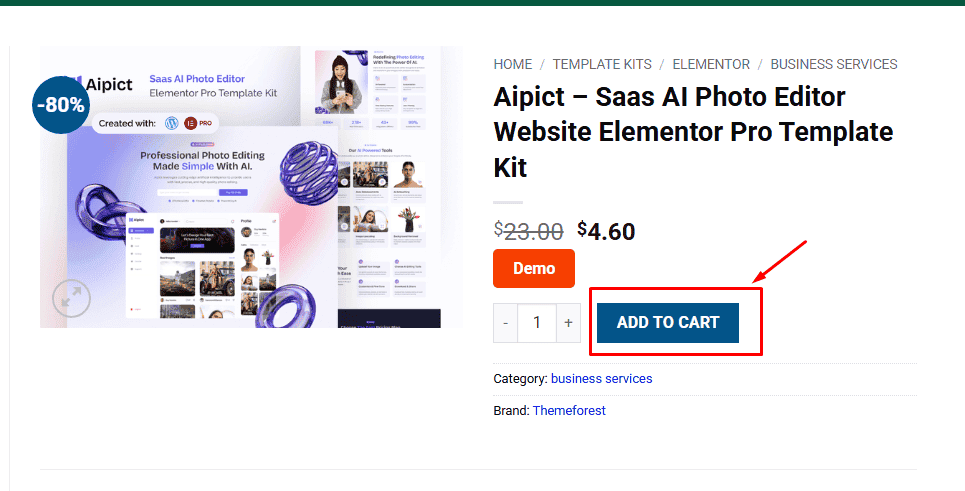
1. Click Add to cart
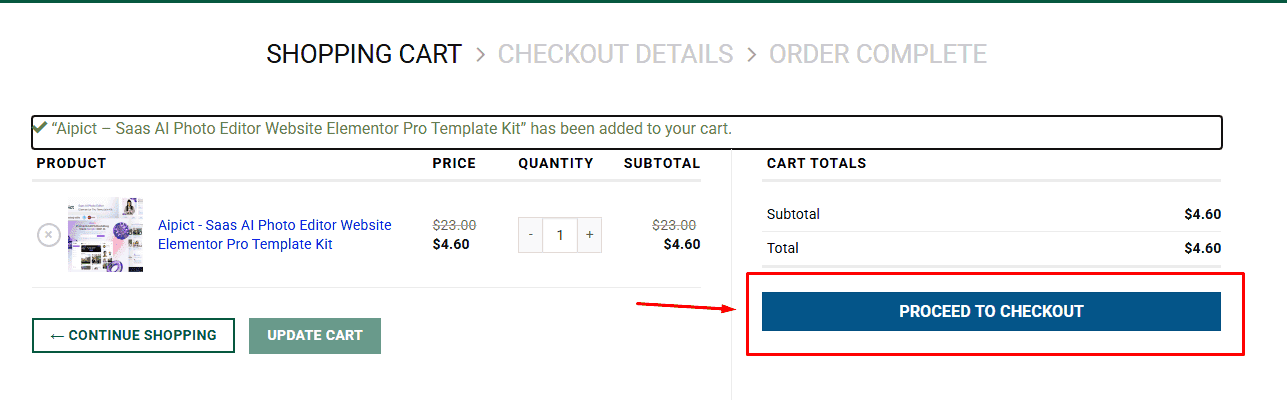
2. Review your items and click Proceed to checkout
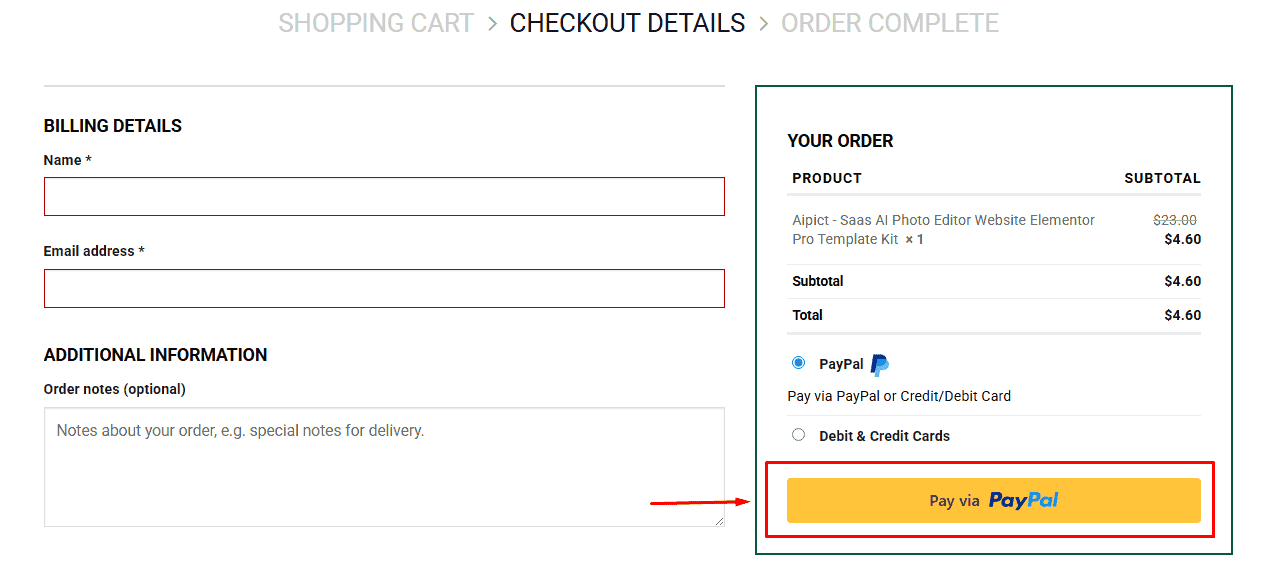
3. Fill in your billing details: Name, Email, and Password
4. Choose your preferred payment method
5. Click Pay via Paypal to proceed
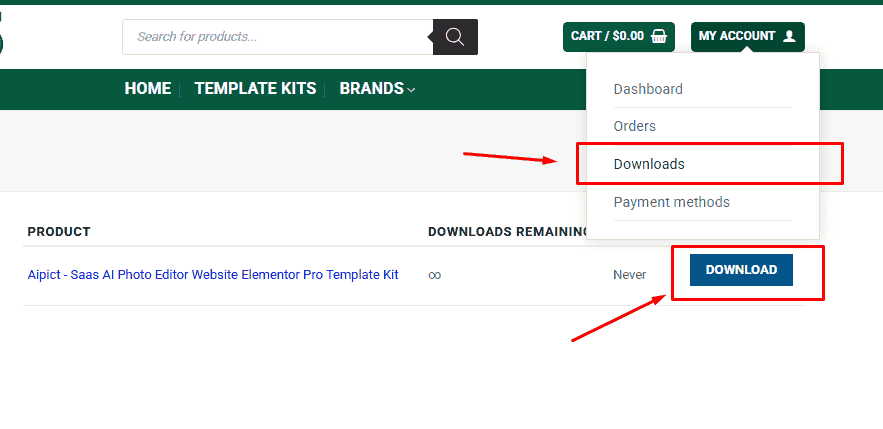
6. Access Downloads to get your files
Related products


